If you have ever written “HIPPA” and then stopped to wonder whether the acronym should have one P or two, you are not alone. The spelling can be surprisingly easy to mix up, especially because HIPPA looks and sounds natural when people say the acronym quickly. Searches such as “hippa or hipaa,” “is it hippa or hipaa,” and “hippa or hipaa in healthcare” all point to the same basic confusion.
The reason is simple: the correct acronym has an unusual letter pattern. HIPAA ends with two A’s, while the commonly misspelled HIPPA contains two P’s. Once you know what the letters represent, the correct form becomes much easier to remember.
In this article, you will learn which spelling is correct, what HIPAA stands for, why HIPPA is incorrect, how the term is used in healthcare, what PHI means, what HIPAA privacy involves, and how the major HIPAA rules fit together.
Is It HIPPA or HIPAA?
HIPAA is correct. HIPPA is incorrect.
The official acronym is:
HIPAA = Health Insurance Portability and Accountability Act of 1996
It is a U.S. federal law enacted in 1996. The law includes provisions concerning health insurance portability as well as administrative simplification, privacy, security, and health information protections. The U.S. Department of Health and Human Services (HHS) identifies the law consistently as HIPAA, with one P and two A’s.
| Form | Correct? | Explanation |
|---|---|---|
| HIPAA | ✅ Yes | Official acronym |
| HIPPA | ❌ No | Common misspelling |
For example:
- ❌ The hospital follows HIPPA regulations.
- ✅ The hospital follows HIPAA regulations.
The same spelling applies whether you are discussing HIPAA laws, HIPAA compliance, HIPAA forms, HIPAA violations, or HIPAA privacy.
What Does HIPAA Stand For?
HIPAA stands for the Health Insurance Portability and Accountability Act of 1996.
The law was enacted as Public Law 104-191 on August 21, 1996. Among other things, HIPAA established requirements related to electronic healthcare transactions and standards, while also leading to federal protections for certain individually identifiable health information.
The acronym can be broken down as:
- H — Health
- I — Insurance
- P — Portability
- A — Accountability
- A — Act
Notice the important detail: there is one P followed by two A’s.
That is why HIPAA, not HIPPA, is the correct spelling.
Why Do People Spell It HIPPA?
The mistake is understandable because HIPPA resembles the spelling patterns people are accustomed to seeing in English. When spoken aloud, the difference between the letters can also be easy to overlook.
There is another reason the error persists: people sometimes remember the beginning HIP and then instinctively add another P, producing HIPPA.
However, acronyms are formed from the words they represent. In Health Insurance Portability and Accountability Act, the relevant letters produce HIPAA, not HIPPA.
Easy Way to Remember the Spelling
Think of the ending this way:
Portability + Accountability = PA + A
So the acronym ends in:
…PAA
Not:
…PPA
A simple visual reminder is:
HIP + AA = HIPAA ✅
HIP + PA = HIPPA ❌
If you are writing a professional healthcare document, report, form, email, or article, use HIPAA.
HIPAA in Healthcare: What Does It Mean?
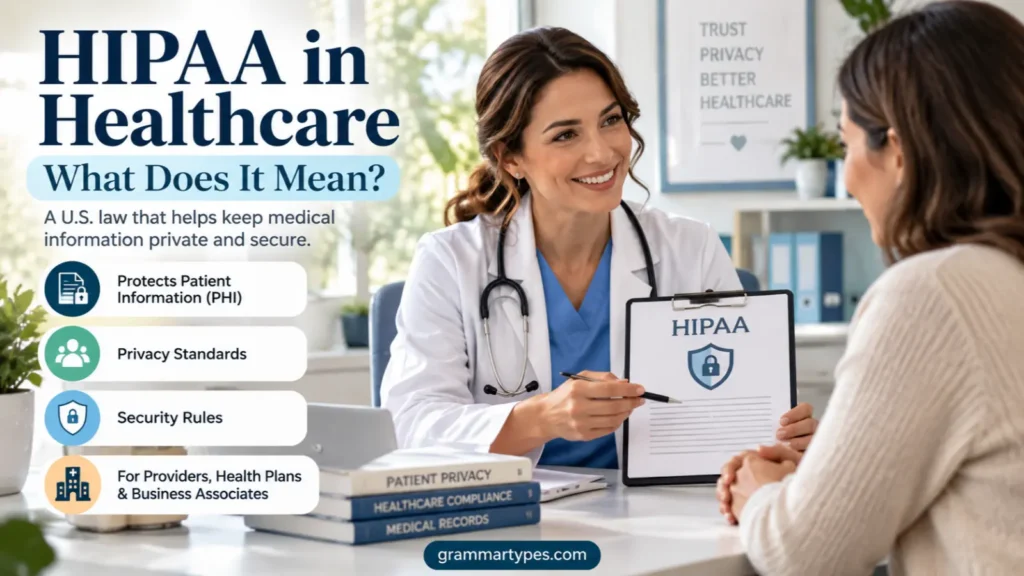
When people search for “hippa or hipaa in healthcare,” they are usually asking about the federal law that governs certain privacy, security, and administrative requirements involving health information.
HIPAA is particularly associated with the protection of protected health information (PHI). The HHS Privacy Rule establishes national standards for protecting certain medical records and individually identifiable health information held by covered entities.
HIPAA applies to certain covered entities, including:
- Health plans
- Health care clearinghouses
- Health care providers that conduct certain standard electronic healthcare transactions
Certain organizations and individuals that perform services for covered entities and have access to PHI may also qualify as business associates and have HIPAA responsibilities.
This is why you may see phrases such as:
- HIPAA compliance
- HIPAA privacy
- HIPAA regulations
- HIPAA violation
- HIPAA-compliant systems
- HIPAA forms
- HIPAA training
In each case, the correct spelling remains HIPAA.
What Is HIPAA Privacy?
HIPAA privacy generally refers to the protections and requirements established by the HIPAA Privacy Rule concerning protected health information.
The Privacy Rule establishes national standards governing certain uses and disclosures of PHI. It also gives individuals rights concerning their health information, including rights to examine and obtain copies of certain health records and request corrections.
For example, HIPAA privacy requirements can affect how a covered healthcare organization handles information about a patient’s:
- Medical condition
- Treatment
- Healthcare services
- Health records
- Payment for healthcare
However, HIPAA does not mean that health information can never be shared. The Privacy Rule permits certain uses and disclosures for purposes such as treatment, payment, and healthcare operations, subject to the applicable requirements.
So saying “HIPAA means doctors can never share your medical information” would be an oversimplification.
What Does PHI Stand for Under HIPAA?
PHI stands for Protected Health Information.
Under HIPAA, PHI generally refers to individually identifiable health information held or transmitted by a covered entity or business associate in circumstances covered by the Privacy Rule. HHS describes PHI as protected health information and explains that the Privacy Rule provides federal protections for personal health information held by covered entities.
Examples can include identifiable information relating to:
- A person’s health condition
- Healthcare received
- Treatment
- Medical records
- Payment for healthcare
The important point is that PHI is not simply every piece of health-related information. Whether information qualifies as PHI depends on the circumstances and the applicable HIPAA definitions and rules.
PHI vs. ePHI
You may also see the term ePHI, meaning electronic protected health information.
The HIPAA Security Rule focuses specifically on protecting electronic PHI and requires appropriate administrative, physical, and technical safeguards to protect its confidentiality, integrity, and availability.
What Are the Main HIPAA Rules?
A common search question is “What are the 5 HIPAA rules?” The answer needs a little clarification because HHS does not define one simple official list containing exactly five universally named “HIPAA rules.”
HHS’s combined regulation text identifies several categories of HIPAA Administrative Simplification regulations, including the Privacy Rule, Security Rule, Enforcement Rule, Breach Notification Rule, Transactions and Code Sets Standards, and Identifier Standards.
The rules most commonly discussed in relation to healthcare privacy and security include:
1. HIPAA Privacy Rule
The Privacy Rule establishes standards for protecting certain individually identifiable health information and regulates permitted uses and disclosures of PHI.
2. HIPAA Security Rule
The Security Rule establishes national standards for protecting electronic PHI. It requires administrative, physical, and technical safeguards designed to protect ePHI.
3. HIPAA Breach Notification Rule
The Breach Notification Rule addresses notifications following breaches of unsecured PHI. Covered entities generally have notification responsibilities when a qualifying breach occurs, with additional requirements depending on the circumstances.
4. HIPAA Enforcement Rule
The Enforcement Rule establishes procedures and standards for enforcing certain HIPAA Administrative Simplification requirements. HHS explains that the Office for Civil Rights enforces the Privacy and Security Rules, while CMS has enforcement responsibilities for various Administrative Simplification requirements.
5. Administrative Simplification Requirements
HIPAA also established standards for electronic healthcare transactions, code sets, and unique identifiers. These requirements help standardize the electronic exchange of healthcare information.
So, if someone asks about the “five HIPAA rules,” it is better to explain the commonly discussed rules while noting that the federal HIPAA regulatory framework contains several distinct categories rather than pretending there is one official five-item list.
Common HIPAA Spelling Mistakes
Because HIPPA is so close to the correct form, it is one of the most common errors people make when writing the acronym.
Mistake 1: Writing HIPPA instead of HIPAA
❌ HIPPA protects patient information.
✅ HIPAA protects certain patient information.
The second sentence uses the official acronym.
Mistake 2: Writing “Hippa”
Capitalization matters less in casual discussion, but when referring to the federal law, the standard form is HIPAA.
❌ Hippa
✅ HIPAA
Mistake 3: Treating HIPPA as a different law
HIPPA is not a separate U.S. healthcare privacy law. It is simply a misspelling of HIPAA.
For example:
❌ “HIPPA is another healthcare privacy regulation.”
✅ “HIPAA is the U.S. federal law associated with these healthcare privacy and security requirements.”
Mistake 4: Assuming HIPAA means only privacy
HIPAA is often discussed in connection with patient privacy, but its scope is broader. The law and its implementing regulations also involve administrative simplification, security, transactions, identifiers, enforcement, and breach notification.
HIPAA vs. HIPPA: Quick Comparison
| Feature | HIPAA | HIPPA |
|---|---|---|
| Correct spelling | ✅ Yes | ❌ No |
| Refers to the U.S. federal law | ✅ Yes | ❌ No |
| Has one P | ✅ Yes | ❌ No |
| Has two A’s | ✅ Yes | ❌ No |
| Used in healthcare | ✅ Yes | ❌ Not as an official term |
| Used in formal writing | ✅ Yes | ❌ Avoid |
The easiest rule is:
HIPAA has one P and two A’s.
Is HIPAA Used in Canada?
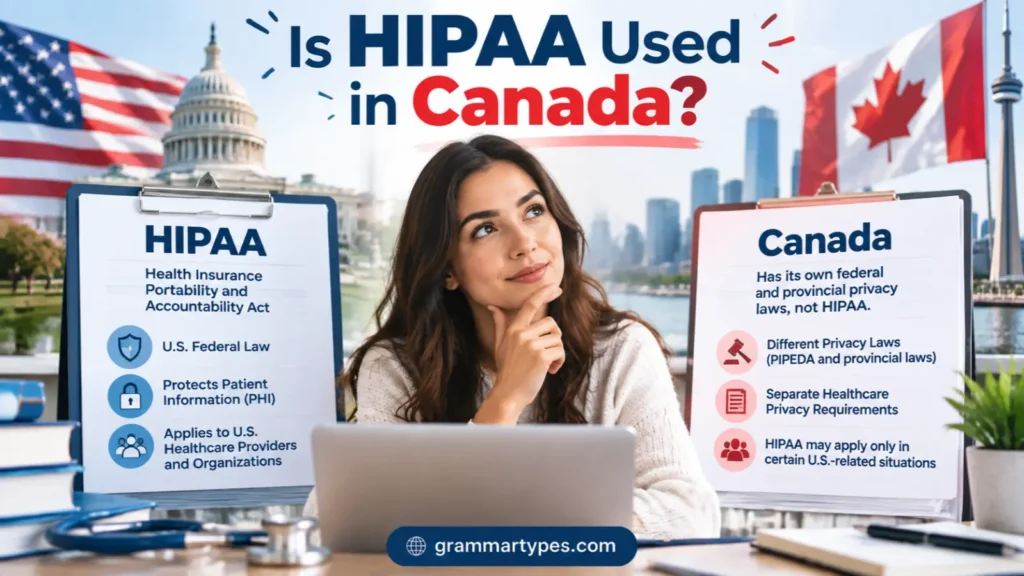
The query “is it hippa or hipaa in Canada” can cause additional confusion because HIPAA is a U.S. federal law.
If you are writing specifically about U.S. healthcare privacy law, the correct acronym is HIPAA regardless of where the writer happens to be located.
Canada has its own federal and provincial privacy laws and healthcare privacy requirements. Therefore, it would be inaccurate to assume that HIPAA is Canada’s general healthcare privacy law simply because the same acronym appears in Canadian healthcare discussions.
If a Canadian organization says it is “HIPAA compliant,” that may refer to a particular business, contract, service, or relationship involving U.S. healthcare information rather than meaning that HIPAA is Canada’s primary privacy statute.
Is “HIPAA Compliant” Correct?
Yes. HIPAA compliant is the standard spelling when describing compliance with applicable HIPAA requirements.
For example:
- ✅ The company offers a HIPAA-compliant platform.
- ✅ The clinic provides HIPAA compliance training.
- ❌ The clinic provides HIPPA compliance training.
Whether an organization or product is actually compliant is a separate legal and factual question. The spelling itself is straightforward: use HIPAA.
Is “HIPAA Form” Correct?
Yes. If you are referring to a form associated with HIPAA requirements, HIPAA form is the correct spelling.
For example:
- HIPAA authorization form
- HIPAA privacy form
- HIPAA compliance form
The phrase “HIPPA form” is simply a misspelled version.
However, not every document described informally as a “HIPAA form” has the same legal purpose. The exact requirements depend on the type of document and the applicable HIPAA rule.
Is HIPAA a Slang Term?
No. HIPAA is not normally a slang term.
The search phrase “HIPAA meaning slang” may appear because people search for the meaning of unfamiliar acronyms, but in standard healthcare usage, HIPAA refers to the Health Insurance Portability and Accountability Act of 1996.
It is a formal legal and healthcare acronym, not a texting abbreviation or internet slang expression.
Quick Memory Trick: HIPAA, Not HIPPA
If you frequently forget which version is correct, remember:
HIPAA = HIP + AA
The ending has two A’s because the final words of the law are:
Accountability Act
So:
HIPAA ✅
HIPPA ❌
You can also remember that HIPAA is the official acronym used by HHS and CMS in their healthcare regulations and guidance.
Final Thoughts
HIPAA is the correct spelling, not HIPPA. The acronym stands for the Health Insurance Portability and Accountability Act of 1996, and it contains one P and two A’s. Although HIPPA is a very common spelling mistake, it is not the official name of the U.S. healthcare law.
When you see terms such as HIPAA privacy, HIPAA compliance, HIPAA violation, HIPAA form, or HIPAA rules, the same spelling applies. HIPAA is also closely connected with PHI, or Protected Health Information, and with regulations covering privacy, security, breach notification, enforcement, and administrative simplification.
The easiest rule to remember is HIP + AA = HIPAA. If you are writing about U.S. healthcare privacy or compliance, choose HIPAA every time.
FAQs
“HIPPA” does not officially stand for anything in this context. It is a common misspelling of HIPAA, which stands for Health Insurance Portability and Accountability Act of 1996.
HIPAA has one P and two A’s. The correct spelling is HIPAA, not HIPPA.
“HIPPA privacy” is a misspelling of “HIPAA privacy.” HIPAA privacy generally refers to the protections and requirements under the HIPAA Privacy Rule concerning certain protected health information.
There is not one official HHS list containing exactly five HIPAA rules. Commonly discussed HIPAA requirements include the Privacy Rule, Security Rule, Breach Notification Rule, Enforcement Rule, and the broader Administrative Simplification requirements. HHS’s combined regulatory framework also separately identifies transactions and code sets and identifier standards.
PHI stands for Protected Health Information. It generally refers to certain individually identifiable health information protected under HIPAA when held or transmitted by covered entities and other regulated parties in applicable circumstances.
Different parts of HIPAA are administered or enforced by different federal agencies. The HHS Office for Civil Rights (OCR) enforces the HIPAA Privacy and Security Rules, while CMS has enforcement responsibilities for various Administrative Simplification requirements, including transactions, code sets, and unique identifiers.
Explore More Grammar Guides:
Puddy or Putty: Which Spelling Is Correct?
Discard or Disgard: Which Spelling Is Correct?
Greatly or Grately: Which Spelling Is Correct? (2026 Guides)
Defence or Defense: Which Spelling Is Correct?(2026 Guides)
